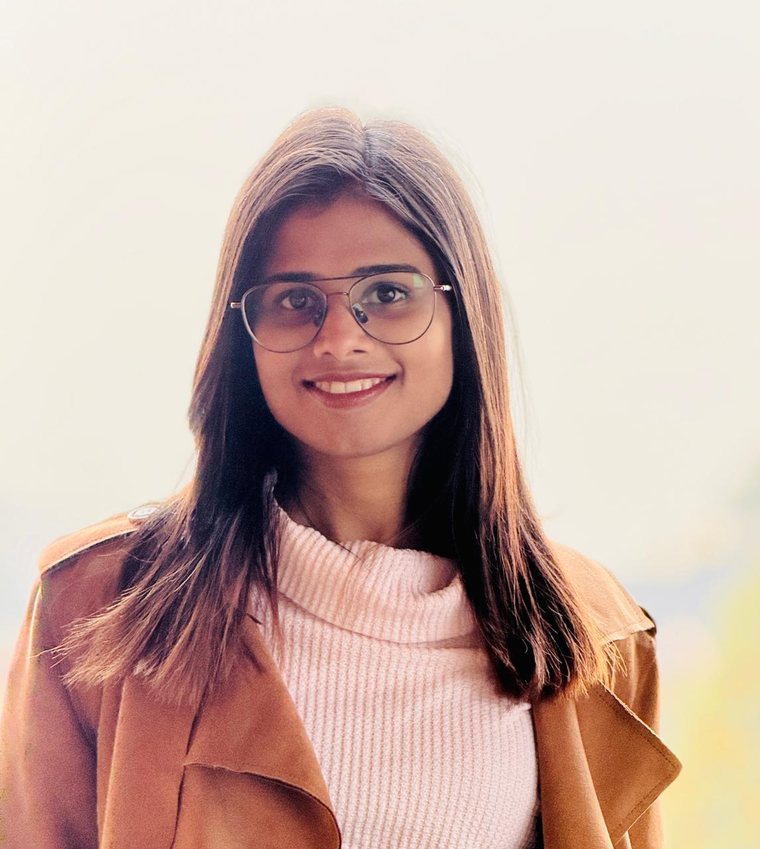
Portrait of Harshita Mittal
Open to work, can join immediately

Harshita Mittal

Cloud security engineer

I lock down cloud infrastructure, then attack the apps running on it. A hardened cloud with a trusting API is still a breach waiting to happen.

3+ yrsin security
AWScloud focus
ISO 27001Lead Auditor
Delhi NCRopen to relocate

Most breaches don't start with a genius exploit. They start with an open port, an over-trusted role, or a server that believes whatever the browser says. I find those first.

Blue team by default. Red team on purpose.

Defense is where I spend most of my time. Offense is how I prove the defense holds.

Primary focus

Defend the cloud

The platform decides how bad any bug can get. I keep AWS small, private and watched, so one mistake stays one mistake.

  • Cloud postureMulti-account AWS audits with Prowler and Wiz, ranked by real risk.
  • Private networkingVPC and Transit Gateway designs with nothing public by accident.
  • Identity and accessIAM and SSO reviews that remove standing admin access.
  • Containers and EKSTrivy image scans and kube-bench CIS checks before release.
  • Detection engineeringWazuh SIEM, file integrity monitoring and Tines automation.
  • Policy as codeCloud and host compliance rules in Rego and OVAL.
AWSWizProwlerRegoOVALTrivykube-benchWazuhSplunkTinesZscaler
Offensive testing

Break the app

Manual web, API and GraphQL testing aimed at the bugs scanners walk past. If the server trusts it, I test it.

  • Web and API testingREST and GraphQL, tested by hand, role by role.
  • Authorization flawsIDOR, broken function-level access and UI-only guards.
  • Tokens and sessionsJWT tampering, session handling and SSO flows.
  • Code and dependenciesBranch protection and dependency triage developers can act on.
Burp Suite ProOWASP ZAPNmapsqlmapNucleiPython

What I hunt for

Scanners find the obvious. These are the questions I ask by hand, on every app I test.

Can a basic user do an admin's job just by calling the API directly?
Broken function-level accessOWASP API5
What happens if I swap this ID for someone else's?
Object-level access (IDOR)OWASP API1
Is the UI hiding a button, or is the server actually saying no?
Client-side trustCWE-602
Is the API sending data the screen quietly masks?
Excessive data exposureOWASP API3
When something fails at 2 a.m., what gets written down?
Secrets in logsCWE-532
Which doors in this account are open to the whole internet, and why?
Cloud misconfigurationCIS AWS

Track record

From watching cloud posture to breaking the apps that run on it.

  1. Jul 2026 to now

    Application Security Engineer

    Financial services company

    VAPT and PCI DSS v4.0.1 self-assessment for CRM, payments and sales apps on AWS, plus cloud audits, EKS reviews and a self-managed Wazuh SIEM.

  2. Jul 2023 to Mar 2026

    Cyber Security Analyst

    TIAA

    Cloud posture with Wiz, compliance rules in Rego and OVAL, then detections and Tines alert workflows on the monitoring team.

  3. Jun to Jul 2022

    Cyber Security Intern

    TIAA

    Built a load-balanced three-server web setup and locked it down with firewall rules.

  4. 2019 to 2023

    B.Tech, Computer Science

    UPES, Cyber Security & Forensics

    Graduated with a CGPA of 8.4.

Interview the terminal

Short on time? Click a question below and the answer shows up right here.

harshita@portfolio: ~

Credentials

ISO/IEC 27001

Lead Auditor

Planning ISMS audits and judging whether controls actually work.

Zscaler

ZDTA

Digital Transformation Administrator: zero trust access and policy.

Also

Zscaler Security Certification

Plus a top 10 finish at the Liba-thon hackathon.

My resume, sealed for you

Everything on this page, on one sheet.

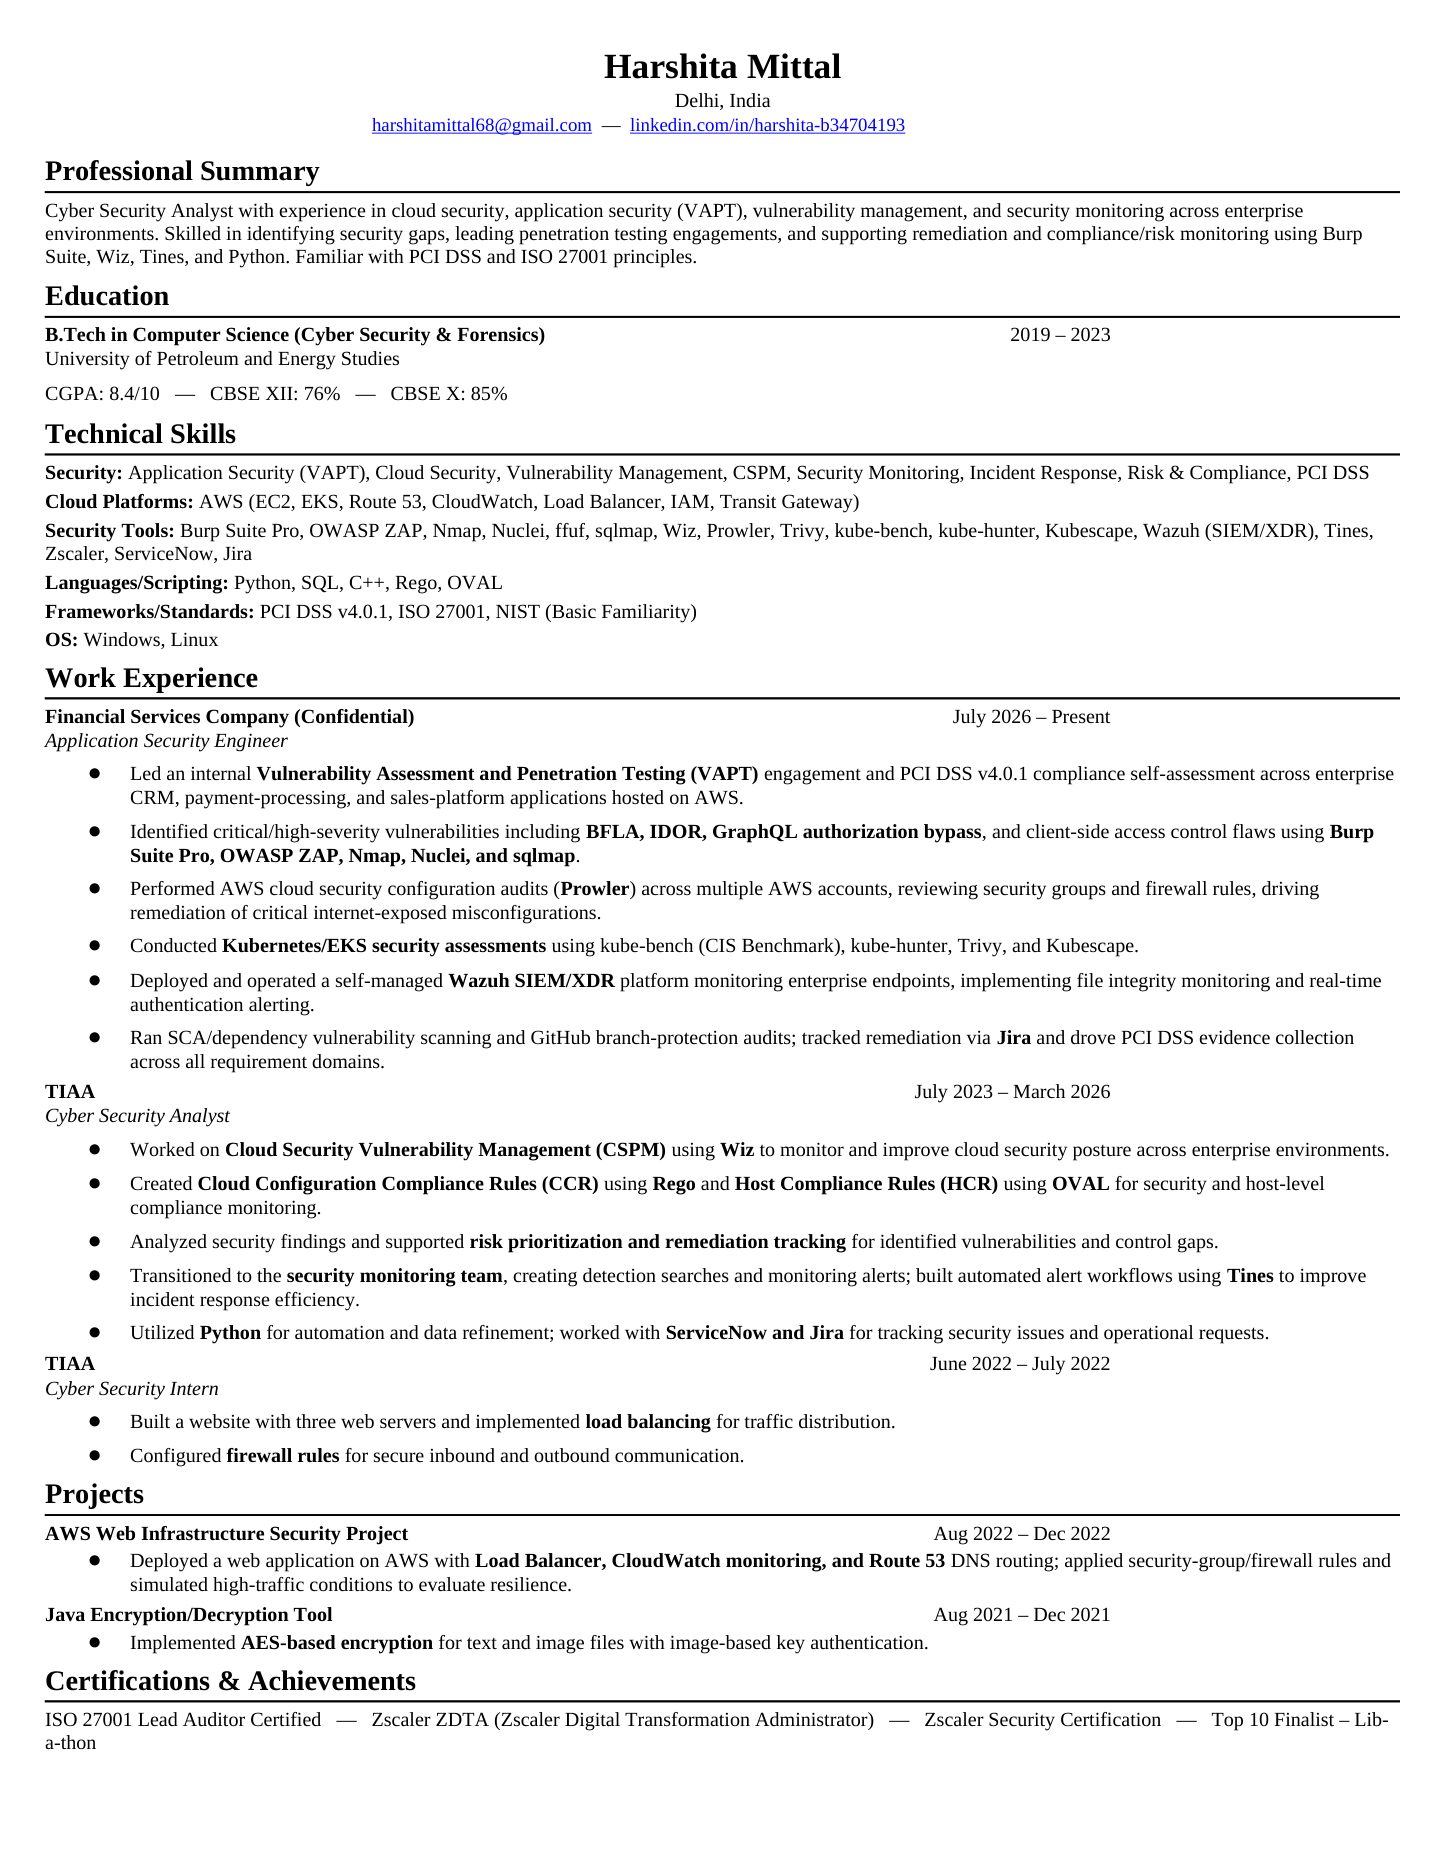
Harshita Mittal's one-page resume

Click the envelope to break the seal

Let's make your cloud boring to attack.

Open to cloud security, AppSec and security engineer roles in Delhi NCR, remote, or somewhere worth relocating to. I can start immediately.

LinkedIn Resume